Security Operations & Managed Services
Security threats don’t take days off. Cyberattacks are growing in volume, sophistication, and cost—yet many organizations still rely on outdated defenses and understaffed IT teams to protect their most critical assets. Security Operations and Managed Security Services offer a structured, scalable solution to this challenge, giving businesses access to enterprise-grade protection without having to build it from scratch.
This guide breaks down how Security Operations Centers (SOCs) work, what Managed Security Service Providers (MSSPs) actually deliver, and how to evaluate whether a managed security partnership is the right move for your organization.
The Threat Landscape Has Changed—Has Your Security Strategy?
The scale of cybercrime today is staggering. According to Cybersecurity Ventures, global cybercrime costs are projected to reach $10.5 trillion annually by 2025, up from $3 trillion in 2015. Ransomware attacks, phishing campaigns, supply chain compromises, and insider threats are no longer isolated incidents—they are everyday realities for businesses of every size.
What makes the modern threat landscape particularly challenging is its pace. Threat actors are faster, better funded, and increasingly automated. A vulnerability disclosed on Monday can be actively exploited by Wednesday. Legacy security tools built for a slower era of threats cannot keep up.
The result? Organizations need more than antivirus software and a firewall. They need continuous monitoring, rapid incident response, and a team of specialists who understand how adversaries think and operate. That’s precisely where Security Operations and Managed Security Services come in.
Core Components of Security Operations
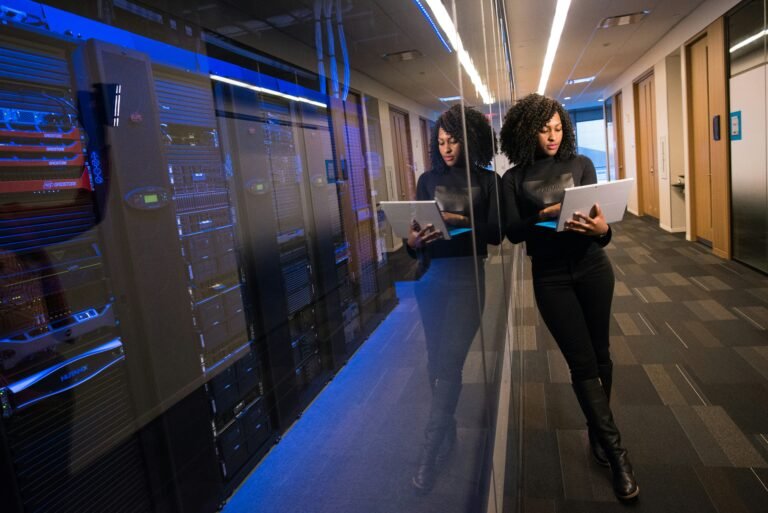
A Security Operations Center (SOC) is the nerve center of any mature cybersecurity program. It combines people, processes, and technology to monitor, detect, analyze, and respond to threats—24 hours a day, 7 days a week.
Threat Detection and Monitoring
At the foundation of every SOC is continuous threat monitoring. Security analysts watch network traffic, endpoint activity, user behavior, and application logs in real time, looking for anomalies that signal a potential breach. The goal is not just to detect attacks after the fact but to identify suspicious behavior early—before it escalates into a full-scale incident.
Effective threat detection relies on a combination of rule-based alerts, behavioral analytics, and threat intelligence feeds that keep pace with the latest attack techniques. Without 24/7 security monitoring, gaps in coverage create windows of opportunity for attackers.
Incident Response and Management
Detection alone does not stop a cyberattack. When a threat is identified, a structured incident response process determines how quickly and effectively an organization can contain the damage, eradicate the threat, and recover normal operations.
A well-defined incident response plan covers everything from initial triage and forensic investigation to communication protocols and post-incident reviews. Speed matters: the average cost of a data breach increases significantly with every hour that passes before containment. According to IBM’s Cost of a Data Breach Report 2023, organizations with an IR team and a tested IR plan saved an average of $1.49 million compared to those without.
Vulnerability Management
Threat detection & incident response are reactive by nature—they deal with threats that are already present. Vulnerability management takes a proactive stance by continuously scanning systems, applications, and infrastructure for known weaknesses before attackers can exploit them.
This includes patch management, configuration audits, and penetration testing to identify gaps that might otherwise go unnoticed. A mature vulnerability management program reduces the attack surface and gives security teams a clearer picture of where risk is concentrated.
Security Information and Event Management (SIEM)
SIEM Implementation & Management is one of the most critical capabilities in modern security operations. A SIEM platform aggregates and correlates log data from across an organization’s entire technology stack—servers, endpoints, cloud environments, firewalls, applications—into a single, unified view.
This correlation capability is what separates a SIEM from basic log collection. By connecting individual data points that might seem innocuous in isolation, a well-tuned SIEM can surface complex, multi-stage attack patterns that would otherwise go undetected. Log management & threat intelligence feeds further enrich this data, providing context on known malicious actors, indicators of compromise, and emerging attack techniques.
The Benefits of Managed Security Services
Building an in-house SOC is a significant investment. It requires specialized talent, advanced tooling, round-the-clock staffing, and continuous training to stay current with an evolving threat landscape. For most organizations, partnering with a managed security services provider (MSSP) delivers faster time to value and a stronger security posture than building in-house.
Access to Deep Security Expertise
The cybersecurity talent shortage is well-documented. According to (ISC)², there are currently more than 4 million unfilled cybersecurity positions globally. MSSPs solve this problem by providing immediate access to a team of experienced analysts, threat hunters, and incident responders—specialists who might be impossible to hire or retain on their own.
This expertise extends beyond general security knowledge. Leading MSSPs maintain dedicated threat intelligence teams that track adversary tactics, techniques, and procedures (TTPs) in real time, ensuring their detection capabilities stay ahead of emerging threats.
24/7 Monitoring Without Gaps
Cyberattacks don’t respect business hours. The majority of ransomware attacks, for example, are carried out on weekends and holidays, when security teams are at reduced capacity. A managed SOC provides continuous, 24/7 security monitoring that eliminates these blind spots—ensuring that threats are detected and escalated regardless of when they occur.
Cost-Effectiveness at Scale
Running a fully staffed, technology-equipped SOC internally can cost millions of dollars annually, including salaries, tools, licensing, and infrastructure. Managed security services convert this into a predictable operational expense, often delivering significantly broader coverage at a fraction of the cost.
Beyond the direct cost comparison, consider the financial risk of a breach. The IBM 2023 report puts the average cost of a data breach at $4.45 million globally. Investing in managed security is, at its core, risk mitigation with a measurable return.
Freedom to Focus on Core Business Priorities
Security operations demand constant attention. Every hour your internal IT team spends investigating alerts is an hour not spent on initiatives that drive the business forward. Partnering with an MSSP removes this burden, freeing internal resources to focus on innovation, growth, and operational priorities.
Key Considerations When Choosing a Managed Security Service Provider
Not all MSSPs are created equal. Selecting the right partner requires careful evaluation across several dimensions.
Service Level Agreements (SLAs)
An SLA defines the standards your MSSP is contractually obligated to meet—detection times, escalation procedures, response times, and uptime guarantees. Before signing any contract, scrutinize these commitments. Vague or weak SLAs are a red flag. Strong providers will offer specific, measurable commitments backed by financial penalties if they fall short.
Technology and Tools
Ask prospective MSSPs about their underlying technology stack. Do they use a modern, cloud-native SIEM? How do they handle SIEM implementation & management for your specific environment? Which log management & threat intelligence sources do they integrate with? The sophistication of their tooling directly impacts the quality of detection and response they can deliver.
Compliance and Certifications
For organizations operating in regulated industries—healthcare, finance, and government—compliance is non-negotiable. Confirm that any prospective MSSP holds relevant certifications such as SOC 2 Type II, ISO 27001, or PCI DSS compliance and that their services support your own regulatory obligations.
Scalability
Your security needs will evolve. As your organization grows, expands into new markets, or adopts new technologies, your MSSP must be able to scale with you. Evaluate whether their service offerings, technology infrastructure, and team capacity can accommodate your growth trajectory without service degradation.
How Businesses Benefit from MSSP Partnerships in Practice
Across industries, the shift to managed security services is producing tangible results. A mid-sized financial services firm that previously relied on a three-person internal IT team for security can, through an MSSP partnership, gain access to a 24/7 SOC, a fully managed SIEM platform, and a dedicated incident response team—thereby immediately improving both detection capabilities and compliance posture.
Retailers facing seasonal surges in transaction volume benefit from the elasticity of managed services, scaling up monitoring capacity during peak periods without permanent headcount additions. Healthcare organizations, where patient data breaches carry both regulatory and reputational consequences, gain continuous oversight that their internal teams cannot maintain on their own.
The common thread: MSSPs deliver security outcomes that would be impractical or impossible to achieve independently.
The Future of Security Operations
How Is AI Changing Threat Detection and Response?
Artificial intelligence and machine learning are reshaping security operations at every level. AI-powered tools can analyze billions of events per day—far beyond human capacity—identifying subtle patterns that indicate sophisticated, slow-moving attacks. Machine learning models trained on historical attack data can predict likely vectors and surface high-confidence alerts, reducing the noise that leads to alert fatigue among analysts.
Automated response capabilities are also advancing rapidly. In well-defined scenarios, AI-driven systems can contain a threat—isolating an affected endpoint, blocking a malicious IP, or revoking compromised credentials—in seconds, long before a human analyst could act.
Proactive Threat Hunting: Moving Beyond Detection
The most advanced security programs no longer wait for alerts to find threats. Proactive threat hunting involves skilled analysts actively searching through data for indicators of compromise that automated systems may have missed. This assumes a breach—operating on the premise that sophisticated adversaries may already be present in the environment—and systematically works to find and eliminate them.
As MSSPs mature, threat hunting is becoming a standard component of premium managed security offerings, moving the industry from reactive to genuinely proactive defense.
Strengthen Your Security Posture Today
The case for security operations and managed security services has never been clearer. Cyber threats are evolving faster than most organizations can manage on their own. The talent gap is real. The cost of a breach is rising. Managed security partnerships address all three challenges simultaneously—delivering expertise, continuous coverage, and cost efficiency that internal programs struggle to match.
Whether your organization is building a security strategy from the ground up or looking to strengthen an existing program, the right MSSP can accelerate your path to a resilient, audit-ready security posture.
Ready to evaluate your options? Start by assessing your current coverage gaps, defining your compliance requirements, and identifying the capabilities—SOC monitoring, SIEM management, and incident response—where external expertise would deliver the greatest impact. The right partner is out there. The right time to find them is now.
Frequently Asked Questions
What is the difference between a SOC and an MSSP?
A Security Operations Center (SOC) is the team and facility responsible for monitoring and responding to security events. A Managed Security Service Provider (MSSP) is an external company that operates a SOC on behalf of its clients. Organizations can build an internal SOC or outsource those functions to an MSSP.
What does SIEM stand for, and why does it matter?
SIEM stands for Security Information and Event Management. A SIEM platform collects and correlates log data from across an organization’s technology environment, enabling security teams to detect complex threats that would otherwise go unnoticed. Proper SIEM implementation & management are central to effective security operations.
How much does a managed security service provider cost?
MSSP pricing varies widely depending on the scope of services, the size of the organization, and the complexity of the environment. Costs typically range from a few thousand dollars per month for small organizations to significantly more for enterprise clients with complex, multi-cloud environments. In most cases, MSSP costs are substantially lower than building and staffing an equivalent internal SOC.
What industries benefit most from managed security services?
Highly regulated industries—including healthcare, financial services, retail, and government—benefit most due to their complex compliance requirements and the sensitivity of the data they handle. However, businesses of all sizes and sectors benefit from the 24/7 coverage and expertise that MSSPs provide.
What should I look for in an MSSP’s SLA?
Look for specific, measurable commitments: mean time to detect (MTTD), mean time to respond (MTTR), escalation timelines, and uptime guarantees. Strong SLAs include financial penalties for missed targets. Avoid providers offering vague or broadly worded service commitments.
How does Log Management support security operations?
Log management involves collecting, storing, and analyzing log data from systems, applications, and network devices. When integrated with threat intelligence feeds, log data becomes a powerful source for detecting indicators of compromise, supporting forensic investigations, and meeting compliance and audit requirements.